Microsoft Ties ConnectWise Breach to China-Linked Hackers Using AI
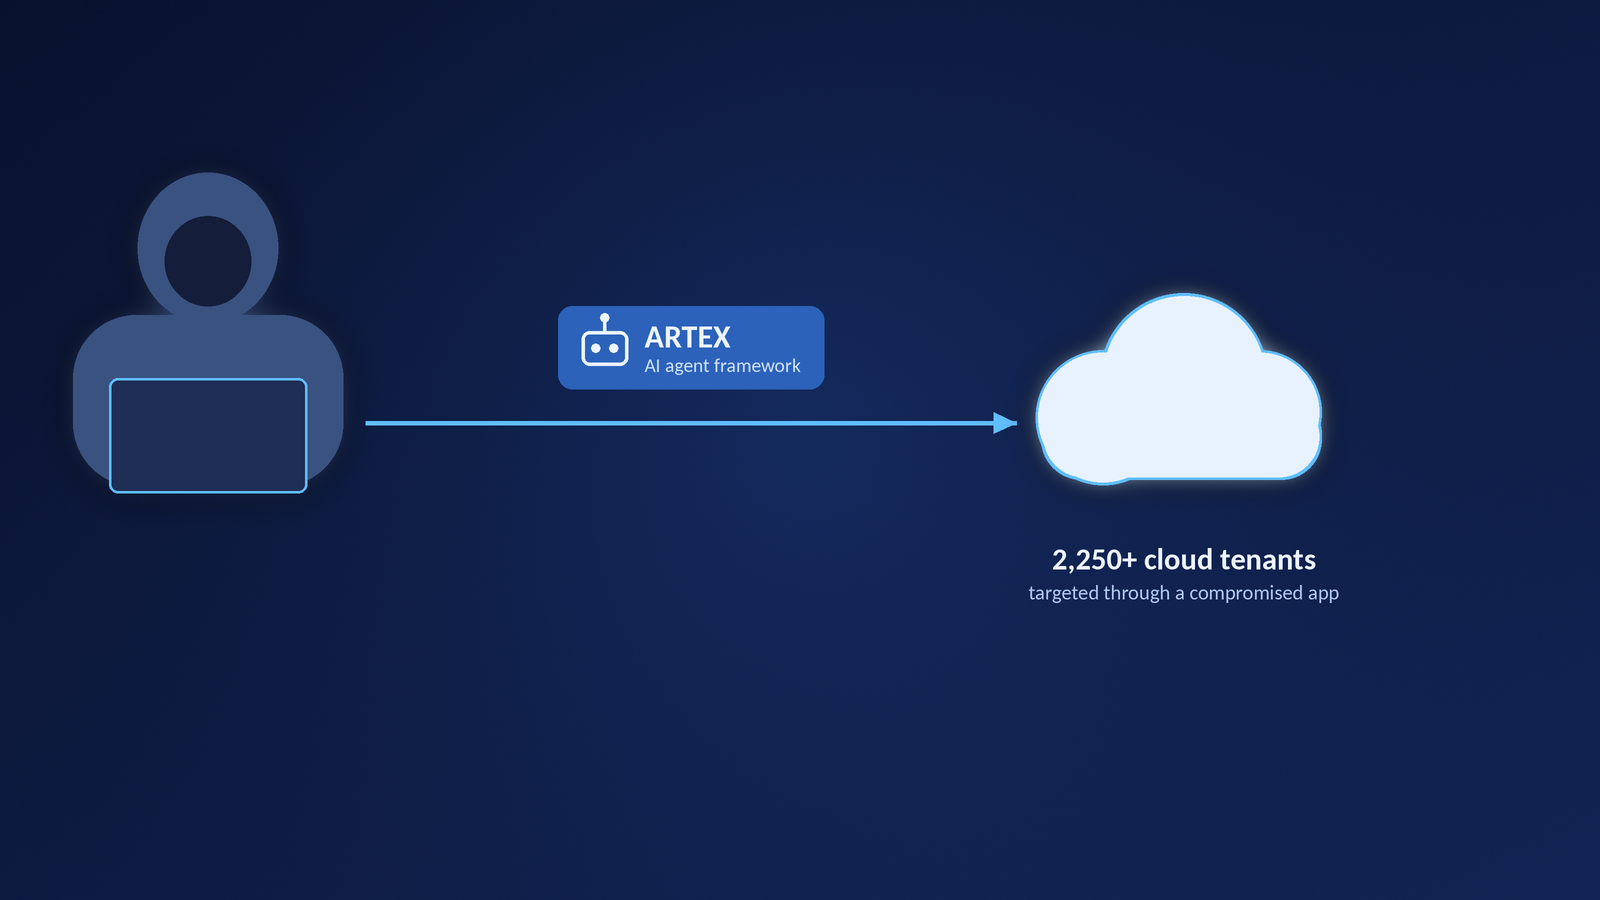
A hacking group Microsoft describes as aligned with the Chinese state has used an open-source AI agent framework called ARTEX to automate attacks on hundreds of organizations since at least September, Microsoft said on Wednesday. Microsoft assesses that the group, which it tracks as Storm-0940, was responsible for the recent supply chain compromise of ConnectWise Cloud Backup, a service IT providers use to back up clients' Microsoft 365 data.
The case shows what changes when attackers hand routine intrusion work to AI agents: they run around the clock and try many routes at once. In several cases, Storm-0940 gained privileged access to an organization's cloud infrastructure in under three hours from first targeting, leaving defenders little time to respond to the alerts the activity triggered.
After obtaining credentials for several ConnectWise cloud applications, the attackers used them to sign in to customer environments as the trusted application, without needing a person to log in. Using ARTEX, they attempted to sign in to more than 2,250 tenants, at a pace of 2,900 sign-in attempts per minute. In some environments, Microsoft says, the agents went on to survey the directory, change application credentials to keep access and alter privileged roles.
While the majority of the targeting wasn't successful, Storm-0940 achieved privileged cloud persistence at many organizations in a brief time,
Microsoft said.
Microsoft cautioned that a successful sign-in does not necessarily mean customer data was accessed or stolen, and said the activity did not stem from a compromise of or vulnerability in its own systems. A ConnectWise spokesperson told The Record there was "no indication" that backup data had been compromised.
Microsoft said it linked the campaign to Storm-0940 by matching IP addresses ConnectWise publicly reported with those seen in its own investigation. ConnectWise temporarily shut down services after the attacks and began restoring them in phases on Wednesday, but did not respond to Microsoft's conclusions about Storm-0940's involvement. The suspended services included Cloud Backup, SaaS Security and Cloud Management.
Storm-0940's other targets spanned aerospace and defense, energy, financial services, government, semiconductors, software, think tanks and other sectors. Microsoft said it has seen threat actors in multiple regions using ARTEX, and security firm Zscaler separately published research on ARTEX abuse the same day, without establishing that it covered the same actor.
Microsoft did not say how many organizations were successfully breached, whether data was taken, or how ARTEX's AI models were supplied.
Microsoft first detailed Storm-0940 in November 2024, when it linked the group to highly evasive password spray attacks run through a botnet called Quad7. The campaign follows CERT-In's warning earlier this month that attackers were using AI offensive-security frameworks to cut attack times from days to hours, though CERT-In did not name specific tools.
Tags
Related Posts
News
SpaceX Agrees to $40 Billion Apollo-Led Lease for Vera Rubin GPUs
2 days ago
News
Anthropic Files for IPO, Posts $16.3 Billion in First-Half Revenue
2 days ago
Risk & Security
OpenAI Bars Internet Access in Frontier Model Training
4 days ago
AI Agents
US Banks Detect Unauthorized AI Agents Inside Customer Accounts
5 days ago